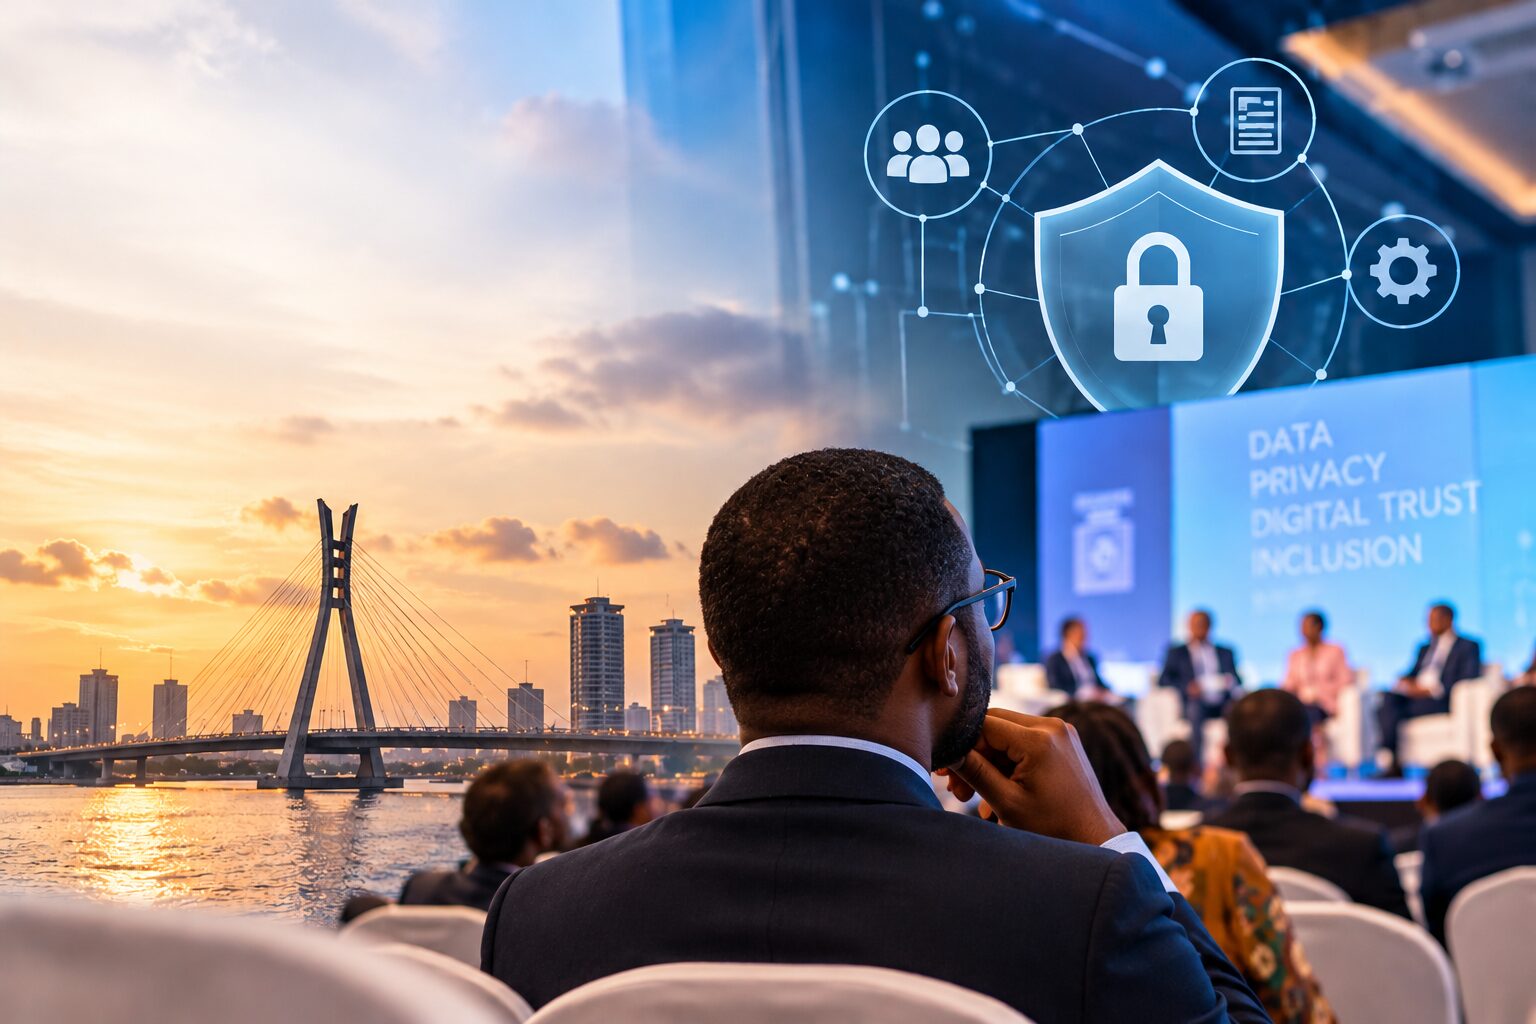
As artificial intelligence (AI) reshapes how organisations work, make decisions, and deliver services, one question becomes increasingly important: what does it take to build digital trust in a data-driven world? This question was at the heart of my reflections during the three-day Data Controllers and Data Processors Conference and Awards in Lagos.
A key takeaway from the conference was that innovation can make organisations faster and more effective, but technology alone doesn’t drive progress. Trust depends on how we manage data, explain decisions, and take responsibility when systems or partners fail.
Against this backdrop, three key lessons stood out for me from the conference, offering practical insights into how organisations can navigate the growing intersection of data protection, artificial intelligence, and digital innovation.
AI can assist, but people remain accountable
AI governance stood out. AI can process large volumes of data, identify patterns, and flag unusual activity. But when an AI recommendation causes harm, who is accountable? Was the problem in the data, the tool, the vendor, or the organisation that acted on its output?
The answer isn’t to reject AI, but to use it within clear boundaries. Organisations need policies defining approved tools, what information employees may enter, and which decisions require human review. Monitor AI for errors and bias, and make its decisions explainable. Staff also need enough subject knowledge to verify AI-generated results.
Data responsibility follows the data
Sessions on cloud services and cross-border transfers showed how information can move beyond an organisation’s direct view. Data may be stored or processed in several locations, while vendors may rely on subcontractors. Organisations need to know what data they hold, where it travels and who can access it.
Accountability cannot simply be handed to a cloud provider or processor. Organisations must assess risks before high-risk processing or international transfers, use appropriate legal safeguards and set clear responsibilities in contracts. Encryption, access controls and data minimisation matter too. Knowing where information is stored is important; knowing who controls it is just as critical.
Due diligence should begin before a contract is signed and continue through regular monitoring. Organisations should ask whether vendors use customer data to train AI models, who their subprocessors are, how breaches are handled, and what happens to data when a relationship ends. Contracts also require active oversight.
Privacy belongs in design and leadership
Privacy should be considered from the earliest stages of product development. Teams should define why they need information before collecting it, gather only what is necessary, and make privacy choices understandable to customers. Product, technical, legal, security, and data protection teams all have a role.
Digital trust also belongs on the leadership agenda. Boards need clear reporting on serious risks, unresolved issues, named owners, and deadlines. Employees need training, secure tools and the confidence to raise concerns.
I left the conference thinking that trust is built through everyday choices: what we collect, which tools we use, how we test them and whether people can question decisions affecting them. For African institutions, it also means helping shape AI and digital solutions that reflect local languages, realities and priorities.
Technology will keep changing. Organisations that pair innovation with transparency, human judgement and accountability will be better placed to earn and keep people’s trust.